Supports digital forensics analysis, including data search and collection,
across a wide range of investigation targets such as servers, desktops, and laptops over a network
Overview
Analysis targets: Desktop, laptop, HDD, SSD, NAS, and more
Supported OS for analysis: Windows OS, Linux, Android, macOS, iOS, Unix, BlackBerry, and more
Supported file systems for analysis: FAT12, FAT16, FAT32, NTFS, HFS, HFS+, UFS, Solaris, AIX, JFS, JFS2, Ext2/3, and more
Results are viewable as analysis progresses, with simultaneous search and analysis across multiple drives and media
Key Functions
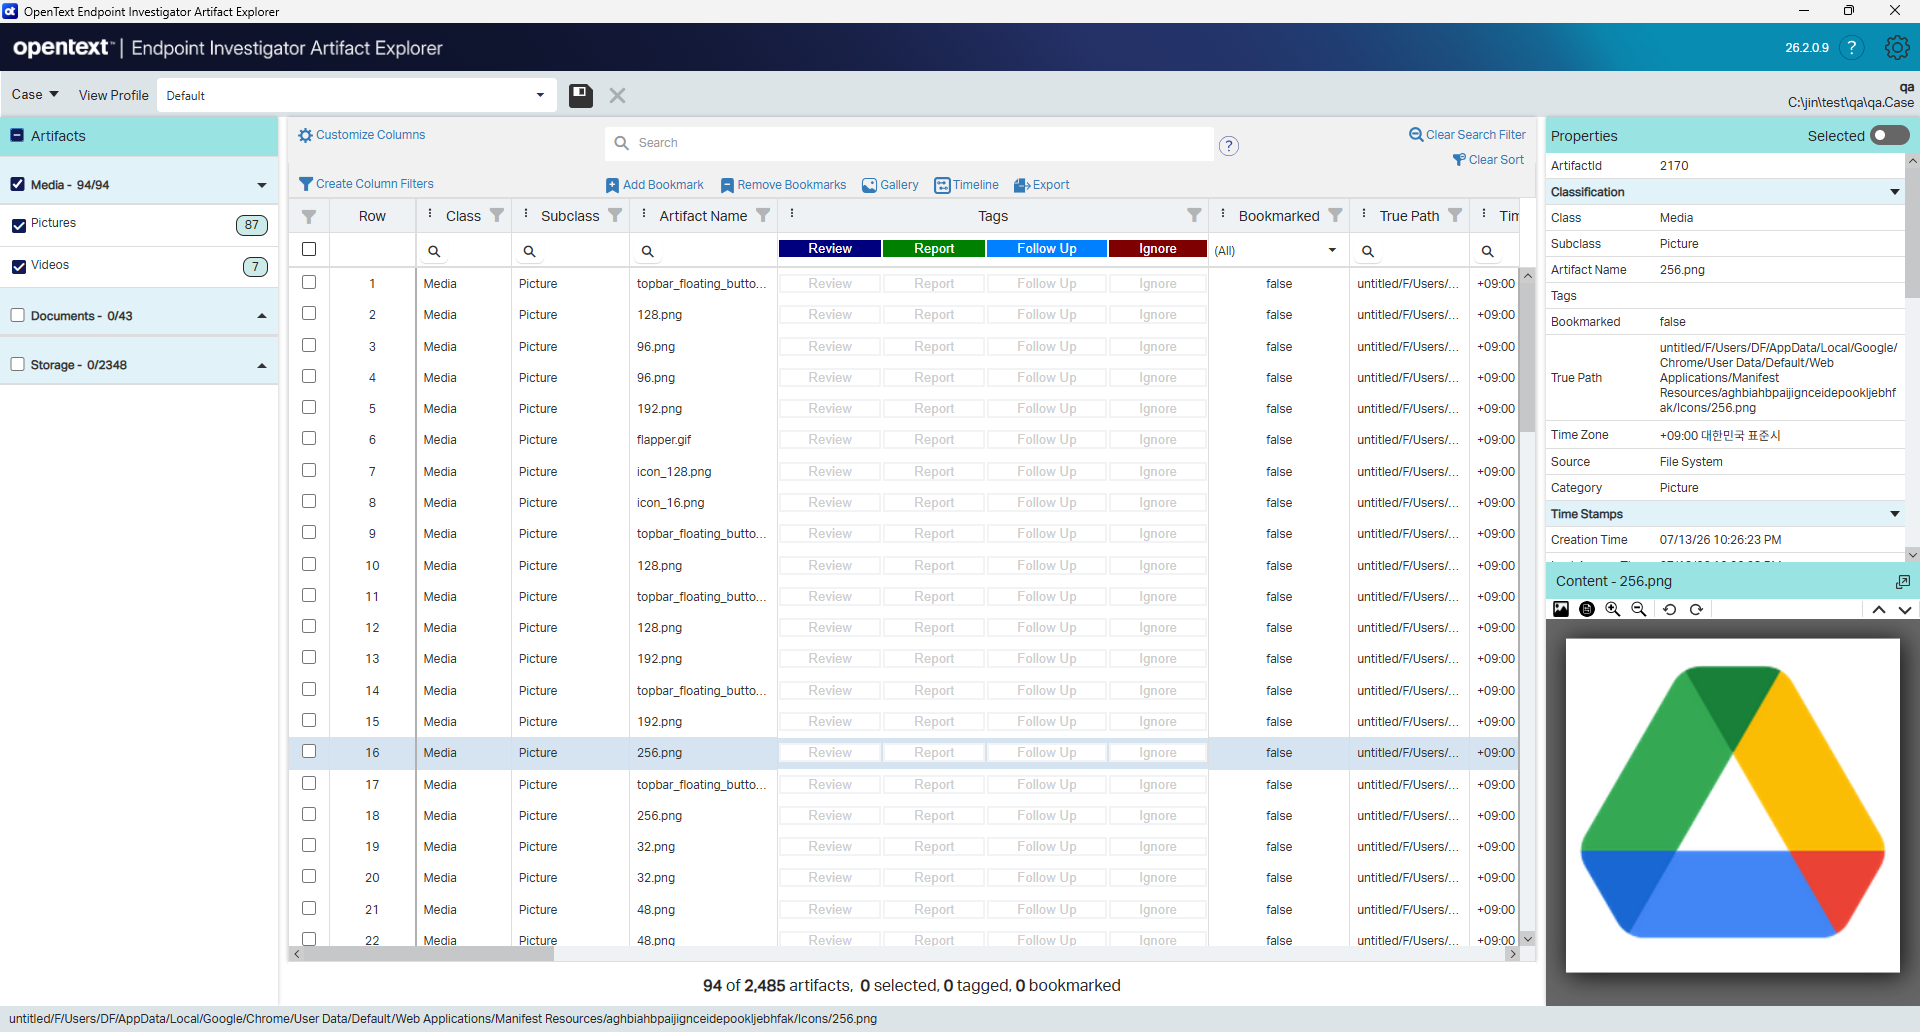
Artifact ExplorerManages system artifacts related to user activity in a customizable format, making it easy for examiners to find the information they need
SnapshotSupports volatile data collection for incident investigation, including running network sessions, open files, and running processes on the system
Network PreviewProvides a network preview feature for quickly reviewing information on remote systems
Sweep EnterpriseScans the analysis target to collect information such as running processes, OS-related artifacts, network activity, and key files