A specialized forensic tool that remotely collects data
from computers and the cloud, and analyzes mobile, IoT, and third-party data
Overview
Purpose: A DFIR tool for targeted collection of endpoint (Mac/Windows/Linux) evidence in remote/off-network environments, through to case analysis
Collection scope: From single physical drive artifacts to volatile memory (RAM)
Output: Collected data is stored in AFF4-L containers
Key Functions
Remote Targeted CollectionSelectively collects only the data you need from remote Mac/Windows/Linux systems (including off-network), automatically resumes if interrupted, and stores results in an AFF4-L forensic container
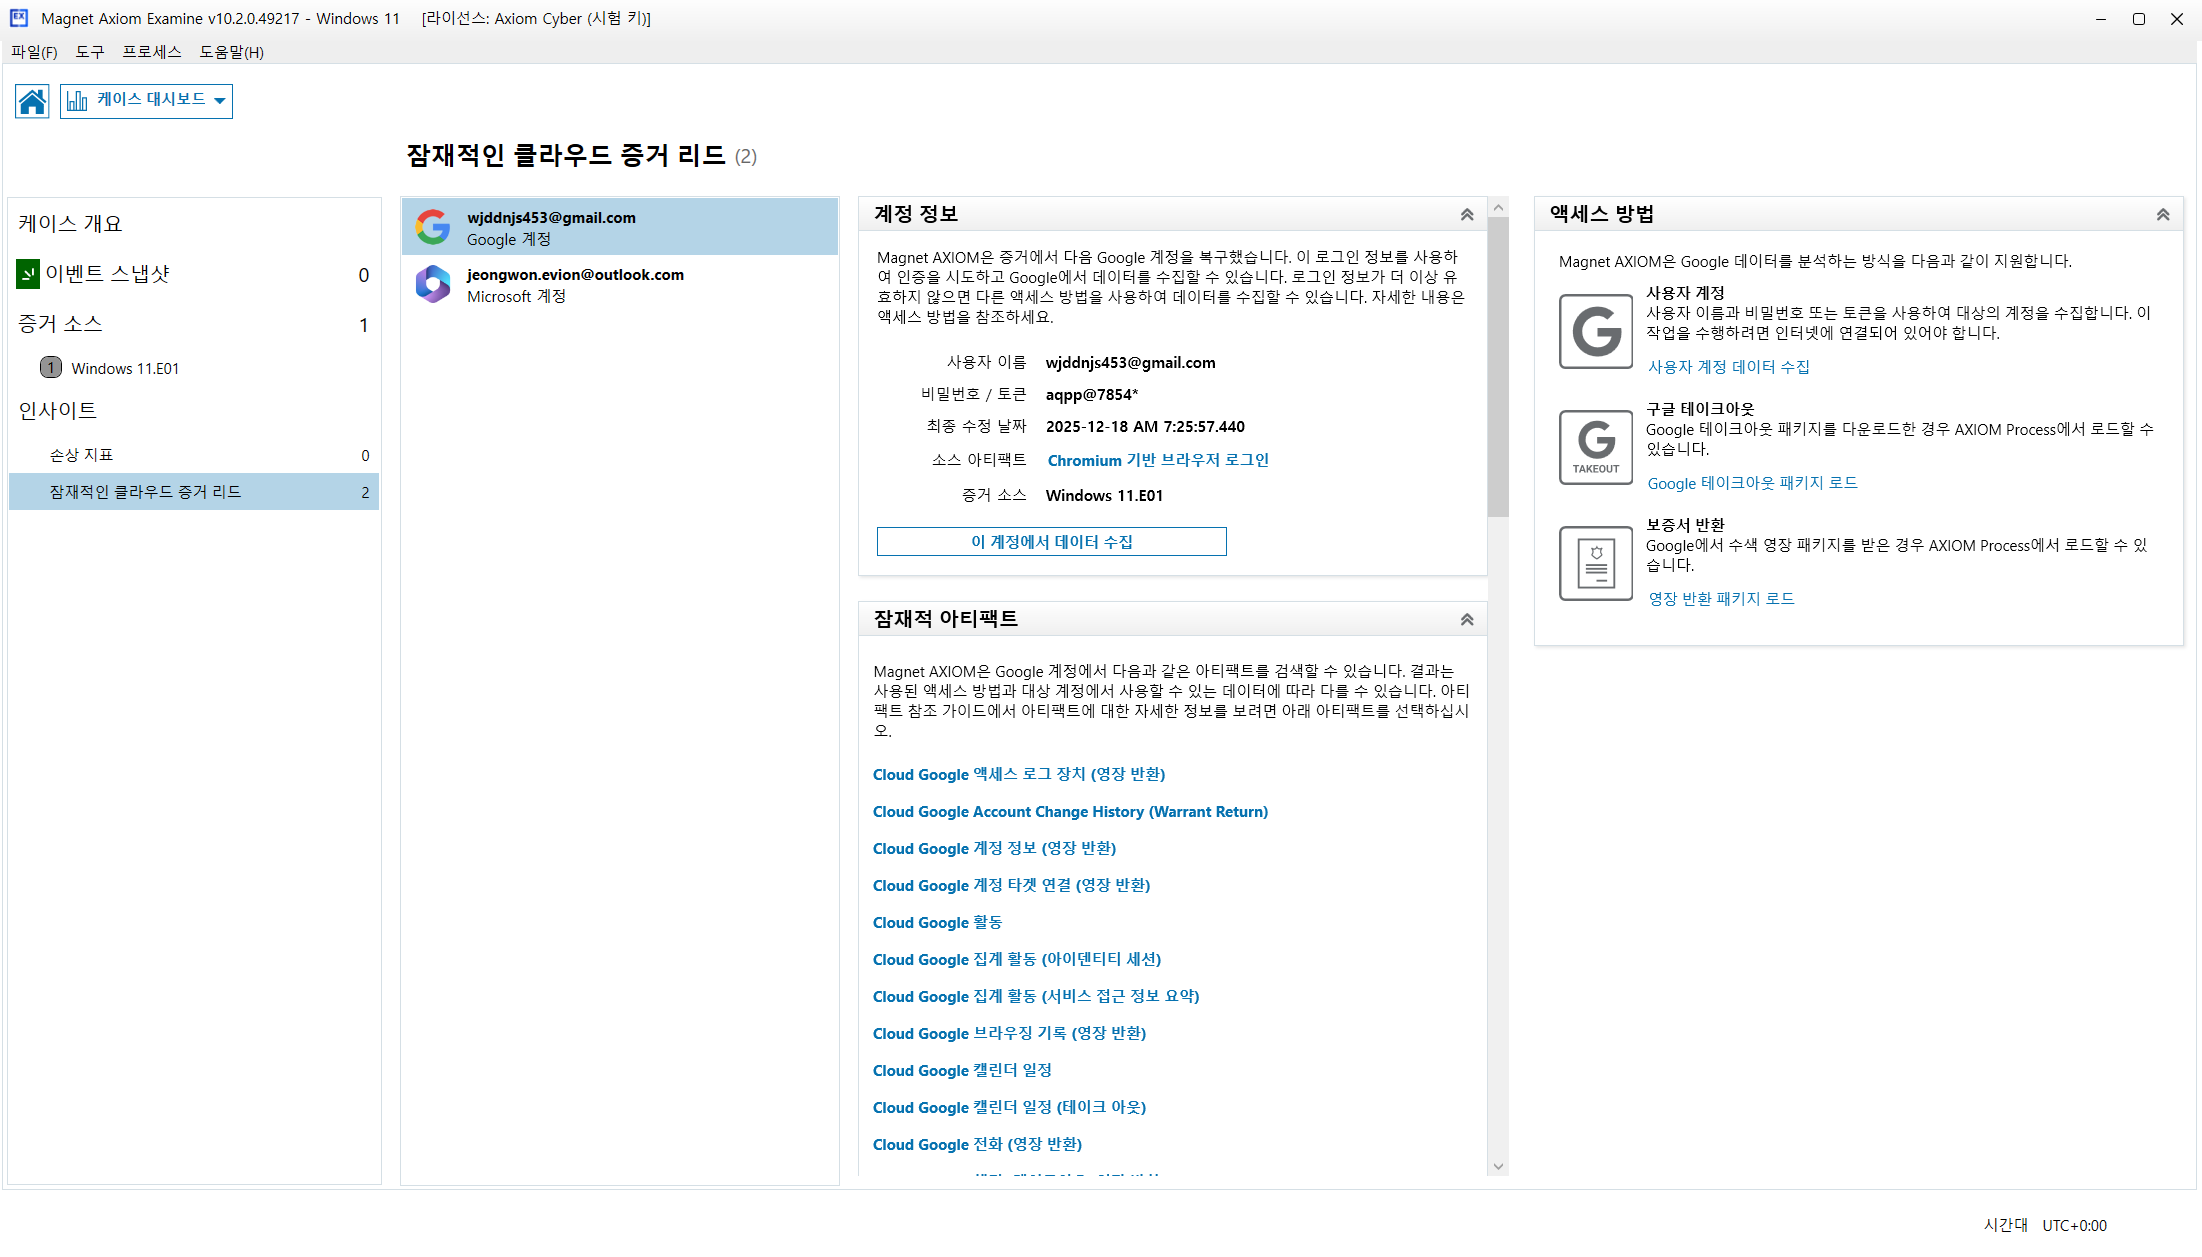
Automatically recovers cloud account information such as Google and Microsoft from evidence, and lets you view account details, potential artifacts, and access methods (user account collection, Google Takeout, warrant return packages) on a single screen, continuing directly into cloud data collection.
※ Key Features and Specifications will be added as materials become available.